Proof of Concept: IACS UR E26/E27 Joint Development Project for Ship Cyber Resilience Testing
## Project Overview
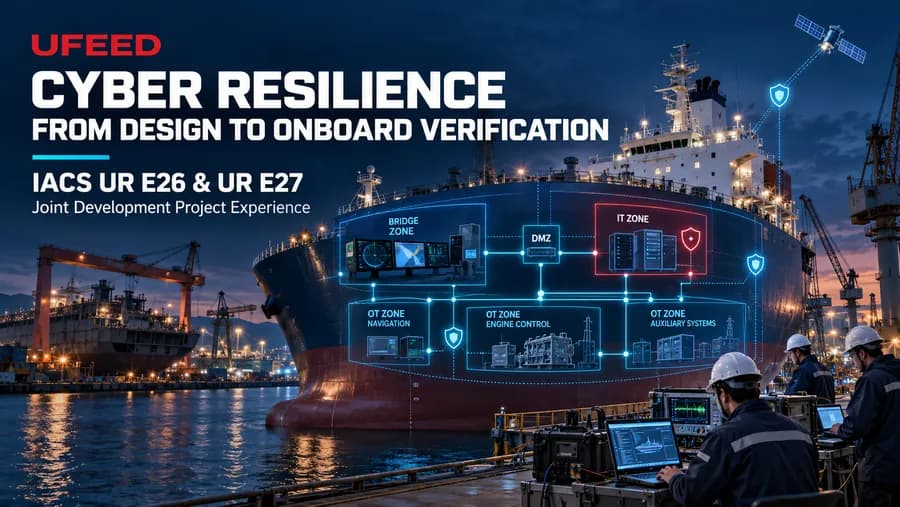
From early to late 2024, UFEED participated in a newbuild Cyber Resilience Joint Development Project (JDP) alongside HD Hyundai Mipo, HD Hyundai Marine Solution (HMS), and Korean Register (KR). The project was designed to meet IACS (International Association of Classification Societies) UR E26 (Cyber Resilience of Ships) and UR E27 (Cyber Resilience of Onboard Systems and Equipment) requirements, covering everything from design-stage documentation review to hands-on cybersecurity testing of actual onboard equipment.
## Project Workflow
**1) Zone & Conduit Diagram / CSDD Development and Class Review**
HMS prepared the Zone and Conduit Diagram and the Cyber Security Design Description (CSDD), which Korean Register reviewed through multiple iterations. Feedback addressed items such as clearly identifying Security Zones, distinguishing managed vs. unmanaged switches, determining whether the DMZ should be treated as a Security Zone or an Untrusted Network Zone, and assessing the need for network monitoring within isolated segments (e.g., the Navi & Radio System Zone). The diagrams were continuously updated based on this feedback.
**2) Establishing the On-Board Test (OBT) Procedure**
Building on the mandatory items specified by KR, the team drafted a Test Procedure and coordinated the detailed schedule — from face-to-face meetings, to pre-tests, to the main test, to final demonstration — through three-way discussions among the shipyard, the design house, and the classification society.
**3) Test Scope and Test Items**
Under the E26/E27 framework, cyber resilience testing is structured around **11 core test items**:
| No. | Test Item | Primary Test Tool |
|---|---|---|
| 1 | Vessel Asset Inventory | Network scanner (NMAP) |
| 2 | Security Zones & Network Segmentation | Network scanner |
| 3 | Network Protection Safeguards | Traffic generator (Hping, Nping) |
| 4 | Anti-virus / Anti-malware Protection | EICAR test file |
| 5 | Access Control | On-site visual inspection |
| 6 | Wireless Communication Security | Protocol analyzer (Wireshark) |
| 7 | Remote Access Control | Protocol analyzer / on-site inspection |
| 8 | Mobile & Portable Device Controls | On-site visual inspection |
| 9 | Network Operation Monitoring | Traffic generator, on-site inspection |
| 10 | Verification & Diagnostic Functions of CBS/Network | On-site visual inspection |
| 11 | Network Isolation | On-site visual inspection |
The equipment under test spanned the vessel's full range of critical systems: main engine remote control (BMS), steering control, generator control, navigation equipment (ECDIS, RADAR, AIS), satellite communication systems (VSAT, Inmarsat), fire detection, and BWTS (Ballast Water Treatment System), among others.
**4) Designing the DoS Load Test — A Practical Engineering Challenge**
Items 3 (Network Protection Safeguards) and 9 (Network Operation Monitoring), which UFEED directly executed, center on Denial-of-Service (DoS) load testing. The test criterion required generating traffic equal to **30–75% of the network's bandwidth, or 100% of the satellite link's bandwidth**. In a 1G network environment, however, laptops limited to a 1500-byte MTU could only generate about 10 Mbps each — making the standard bandwidth target physically impractical to reach with the available hardware.
To solve this, UFEED **reframed the attack target around the actual bandwidth of the VSAT satellite link**, allowing the test to meet its criteria realistically with a small number of devices. This kind of field-level problem-solving was key to producing reliable, defensible test results within tight equipment and schedule constraints.
**5) On-Site Testing and Demonstration**
At the test site in Busan, physical equipment was tagged and labeled to match the asset inventory, followed by pre-testing, procedure-based main testing (repeated across four or more cycles), and a final demonstration. The full process and results were documented, along with a summary report, for use as classification approval evidence.
## Key Takeaways
This JDP illustrates that maritime cyber resilience is not merely a paperwork exercise — it is an **integrated process linking design, certification, and field verification**. Building on its IT infrastructure, network, and security assessment expertise, UFEED has developed hands-on experience designing and executing cyber resilience tests applicable to real onboard environments — a capability now being extended to shipyards and shipowners preparing for IACS UR E26/E27 compliance.
- maritime-cybersecurity
- IACS-E26
- IACS-E27
- JDP
- Cyber-Resilience
- zone-and-Conduit-Diagram
- Dos-Test